44 pci dss antivirus requirements
Official PCI Security Standards Council Site - Verify PCI Compliance ... Just published: PCI Secure Software Standard v1.2 Version 1.2 introduces the Web Software Module, a set of supplemental security requirements to address the most common security issues related to the use of internet-accessible payment technologies. Read More Just Announced: PCI DSS v4.0 Reporting Updates What Is PCI Compliance? Everything You Need To Know PCI compliance standards require merchants to consistently adhere to the PCI Standards Council's guidelines known as the Payment Card Industry Data Security Standard (PCI DSS). These...
PCI DSS Requirements - PCI DSS GUIDE PCI DSS Requirement 2.3: Encrypt all non-console administrative access to devices using strong encryption. Use technologies such as SSH, VPN or SSL / TLS for all web-based and non-console other administrative access.
Pci dss antivirus requirements
The 12 PCI DSS Requirements: 4.0 Compliance Checklist - Varonis It's not enough to simply install basic antivirus software to be PCI-DSS compliant. You need to update and patch your antivirus software applications on a regular basis. This PCI security standard is designed to guard against malware and any number of viruses that could compromise your systems and cardholder data. Payment Card Industry Data Security Standard - Wikipedia The Payment Card Industry Data Security Standard ( PCI DSS) is an information security standard used to handle credit cards from major card brands. The standard is administered by the Payment Card Industry Security Standards Council, and its use is mandated by the card brands. It was created to better control cardholder data and reduce credit ... Official PCI Security Standards Council Site - Verify PCI Compliance ... The PCI Data Security Standard (PCI DSS) applies to all entities that store, process, and/or transmit cardholder data. It covers technical and operational practices for system components included in or connected to environments with cardholder data. If you accept or process payment cards, PCI DSS applies to you.
Pci dss antivirus requirements. Anti-Virus Security - PCI DSS Security PCI DSS Requirement 5 Anti-Virus Security Category: Anti-Virus Security Anti-Virus Security solutions are typically software agents that provide a mechanism to protect systems from malicious software or malware. Typically these systems utilize regularly updated malware databases and heuristic methods to identify malware. PCI Solution Provider Home - PCI DSS GUIDE Popular data security articles: the most-read PCI DSS compliance and data security posts. Documentation The Best Information Security Guide for Students 2023. ... The PCI DSS requirements apply to all system components, including people, processes and technologies that store, process or transmit cardholder data or sensitive authentication data ... What are the 12 requirements of PCI DSS Compliance? - ControlCase PCI DSS Requirement 1: Install and maintain a firewall configuration to protect cardholder data This first requirement ensures that service providers and merchants maintain a secure network through the proper configuration of a firewall as well as routers if applicable. Properly configured firewalls protect your card data environment. PCI DSS - Azure Compliance | Microsoft Learn Azure and PCI DSS. Microsoft Azure maintains a PCI DSS validation using an approved Qualified Security Assessor (QSA), and is certified as compliant under PCI DSS version 3.2.1 at Service Provider Level 1. The Attestation of Compliance (AOC) produced by the QSA is available for download. If you want to develop a cardholder data environment (CDE ...
What is PCI DSS | Compliance Levels, Certification & Requirements | Imperva PCI DSS requirements. The PCI SSC has outlined 12 requirements for handling cardholder data and maintaining a secure network. Distributed between six broader goals, all are necessary for an enterprise to become compliant. ... Anti-virus software must be used and regularly updated; Secure systems and applications must be developed and maintained ... Denis Ahimbisibwe - PCI-DSS Compliance Analyst - Remote - Baxter Clewis ... IT Risk,Legal & Compliance Analyst. Jan 2023 - Present4 months. New York, NY 10014. Creating initial security policies and deploy controls in accordance with NIST, PCI-DSS, and CIS benchmarks ... What are the 12 requirements of PCI DSS Compliance? - SecurityMetrics PCI REQUIREMENT 1: Install and Maintain Network Security Controls. Install a hardware and software firewall Tweak firewall configuration for your system Have strict firewall rules PCI REQUIREMENT 2: Apply Secure Configurations to All System Components. Protect Account Data Maintain a Vulnerability Management Program. Avoid using default passwords PCI Requirement 5: Protecting Your System with Anti-Virus - SecurityMetrics PCI DSS requires anti-virus to be installed on all systems that are commonly affected by malware (e.g., Windows). Beyond financial requirements, anti-virus software also offers an additional layer of security to any system within a network.
What Is PCI DSS? - Compliance, Definition, Levels & More - Proofpoint Payment Card Industry Data Security Standard (PCI-DSS) is a list of compliance standards containing policies around protecting consumer payment and financial data. Organizations must follow PCI-DSS compliance when they store payment information from consumers or risk paying hefty fines for violations. The standards council offers a security ... PCI-DSS Compliance | Cybersecurity | CompTIA Created by the PCI - Security Standards Council (PCI-SSC), the standard works toward increasing protection and controls around cardholder data while reducing the risk of credit card fraud at the same time. If your organization is PCI compliant, it demonstrates major progress in your efforts toward preventing data breaches and cyberattacks. Protecting Your System with Anti-Virus: PCI DSS Requirement 5 For PCI DSS antivirus compliance, you must meet the following requirements: Anti-virus software must be installed on all components covered by the PCI DSS and are commonly affected by viruses. The anti-virus solution must detect, remove, and protect against all malware types, such as Trojans, worms, spyware, adware, and rootkits. Payment Card Industry (PCI) Data Security Standard (DSS) The Payment Application Data Security Standard (PA DSS) is a set of requirements that comply with the PCI DSS, and replaces Visa's Payment Application Best Practices, and consolidates the compliance requirements of the other primary card issuers.
PCI DSS Compliance Requirements Guide & Checklist | Sucuri
PCI DSS Compliance Requirements Guide & Checklist | Sucuri PCI Requirement 2 states that you should not use vendor-supplied defaults for system passwords and other security parameters. By fulfilling requirements 1 and 2 of the PCI DSS, you are meeting the goal to build and maintain a secure network. Here are our suggestions for fulfilling PCI Requirement 2:
PCI Requirement 5.1 – PCI Demystified with Jeff Wilder ...
PCI DSS explained: Requirements, fines, and steps to compliance PCI DSS stands for Payment Card Industry Data Security Standard. Companies can demonstrate that they've implemented the standard by meeting the reporting requirements laid out by the...

Analysis of PCI DSS v4.0 - Part 4: Requirements 5 & 6
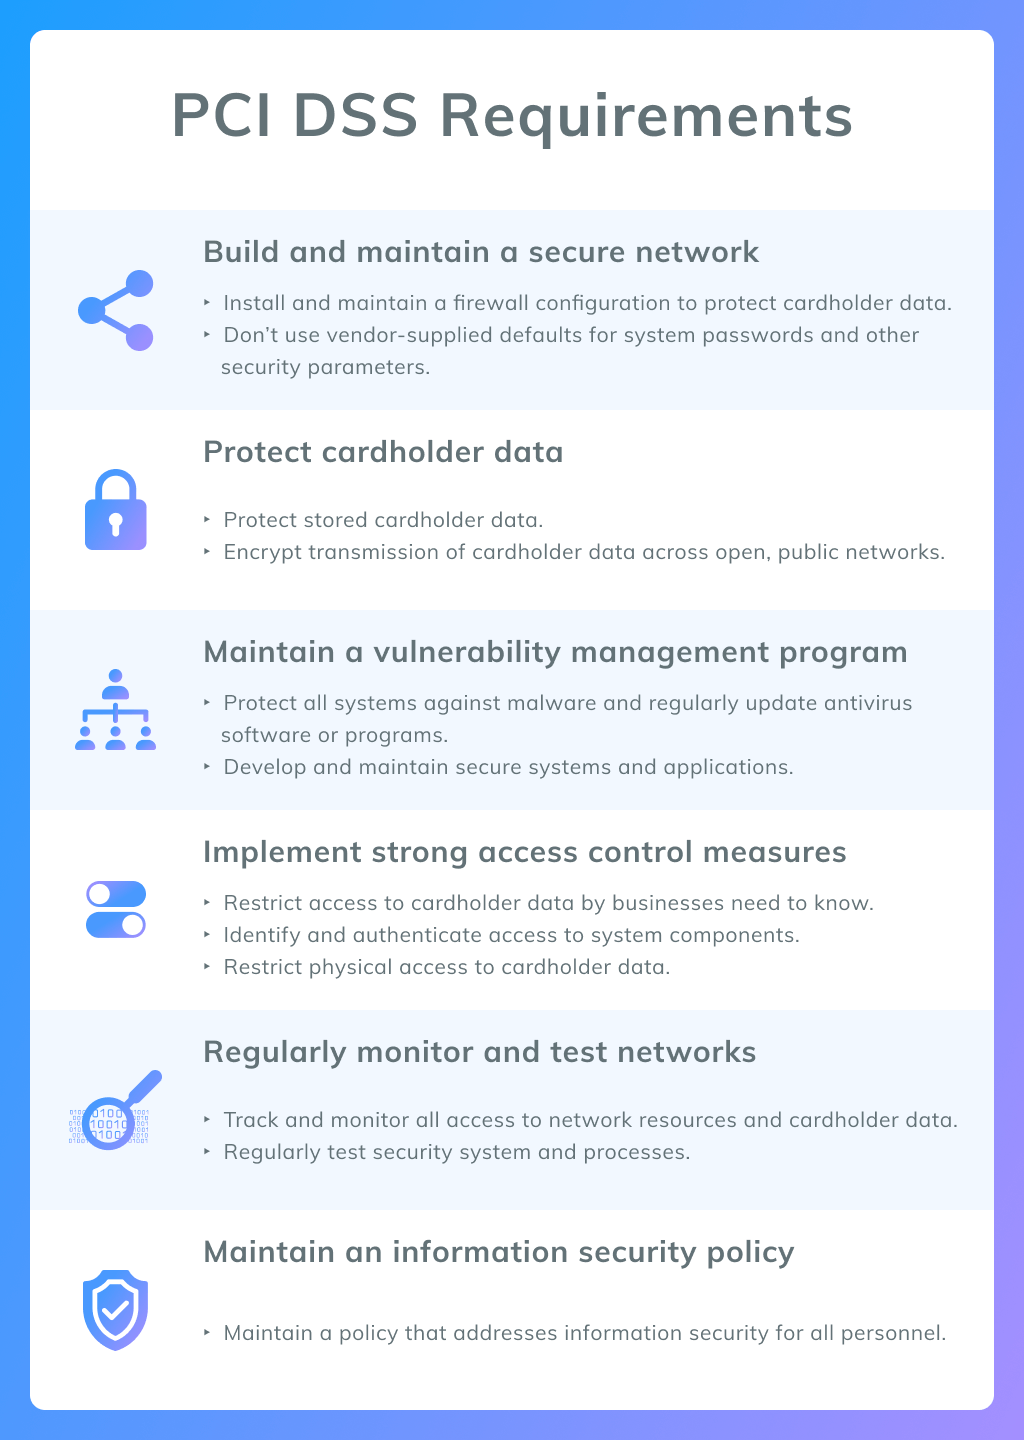
PCI DSS Overview. What are The Requirements for Compliance with This ... PCI DSS has 12 core security requirements. They can be divided into six groups. Organizations implementing this standard must: protect their corporate network. Configure your firewall and...
eCommerce PCI Compliance: Full Guide — GoMage Blog
PCI DSS Cybersecurity Requirements: A Practical Guide The PCI DSS includes several requirements related to cybersecurity, including installing and maintaining a firewall, encrypting the transmission of cardholder data, using and regularly updating antivirus software, developing and maintaining secure systems and applications, assigning user access identification, tracking, and monitoring network …

Comparison of PCI DSS and ISO/IEC 27001 Standards
Official PCI Security Standards Council Site - Verify PCI Compliance ... The PCI Data Security Standard (PCI DSS) applies to all entities that store, process, and/or transmit cardholder data. It covers technical and operational practices for system components included in or connected to environments with cardholder data. If you accept or process payment cards, PCI DSS applies to you.
VMware Site Recovery for VMware Cloud on AWS is now PCI DSS ...
Payment Card Industry Data Security Standard - Wikipedia The Payment Card Industry Data Security Standard ( PCI DSS) is an information security standard used to handle credit cards from major card brands. The standard is administered by the Payment Card Industry Security Standards Council, and its use is mandated by the card brands. It was created to better control cardholder data and reduce credit ...
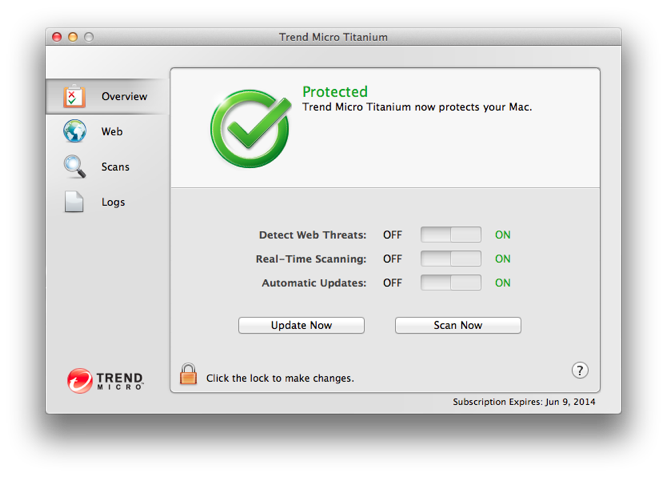
Anti-virus for Mac for PCI Compliance
The 12 PCI DSS Requirements: 4.0 Compliance Checklist - Varonis It's not enough to simply install basic antivirus software to be PCI-DSS compliant. You need to update and patch your antivirus software applications on a regular basis. This PCI security standard is designed to guard against malware and any number of viruses that could compromise your systems and cardholder data.

AspDotNetStorefront and PCI DSS requirements

PCI DSS Compliance Checklist & Requirements in 2021 | Rivial

PCI DSS: Compliance , Certification & Requirements
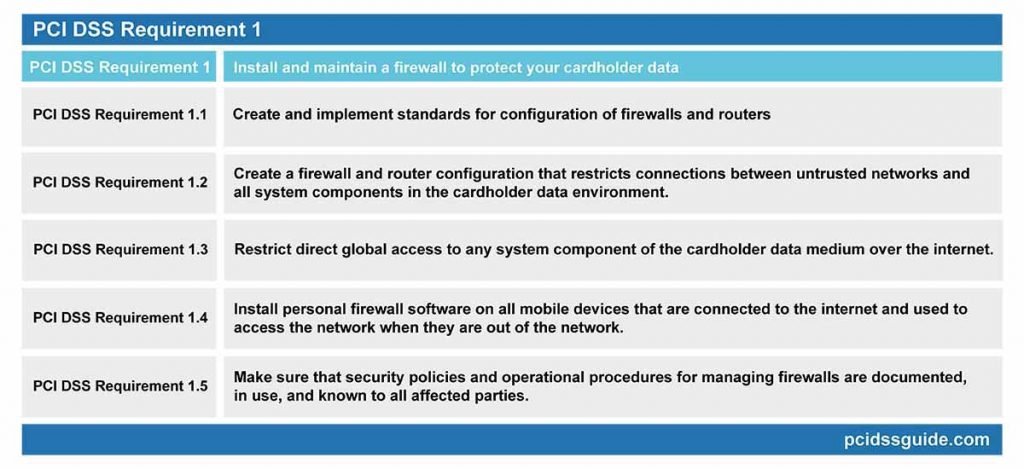
PCI DSS Requirements - PCI DSS GUIDE
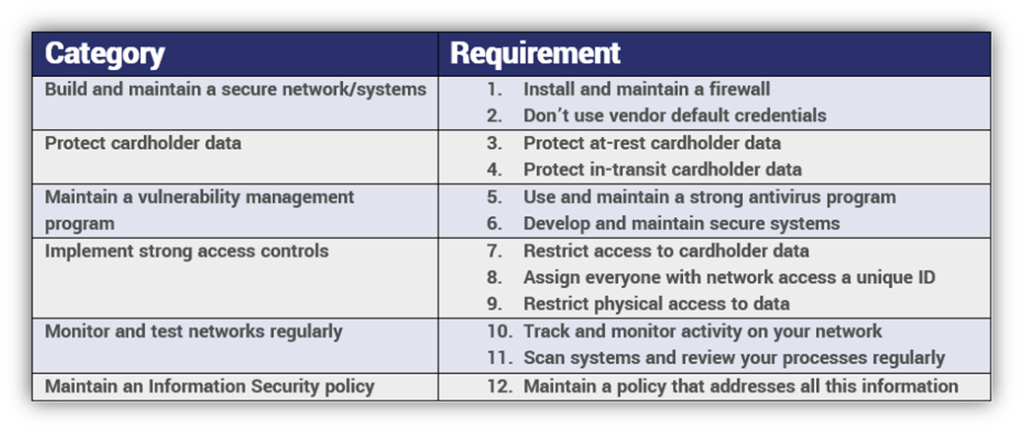
Demystifying PCI DSS Compliance - Hashed Out by The SSL Store™
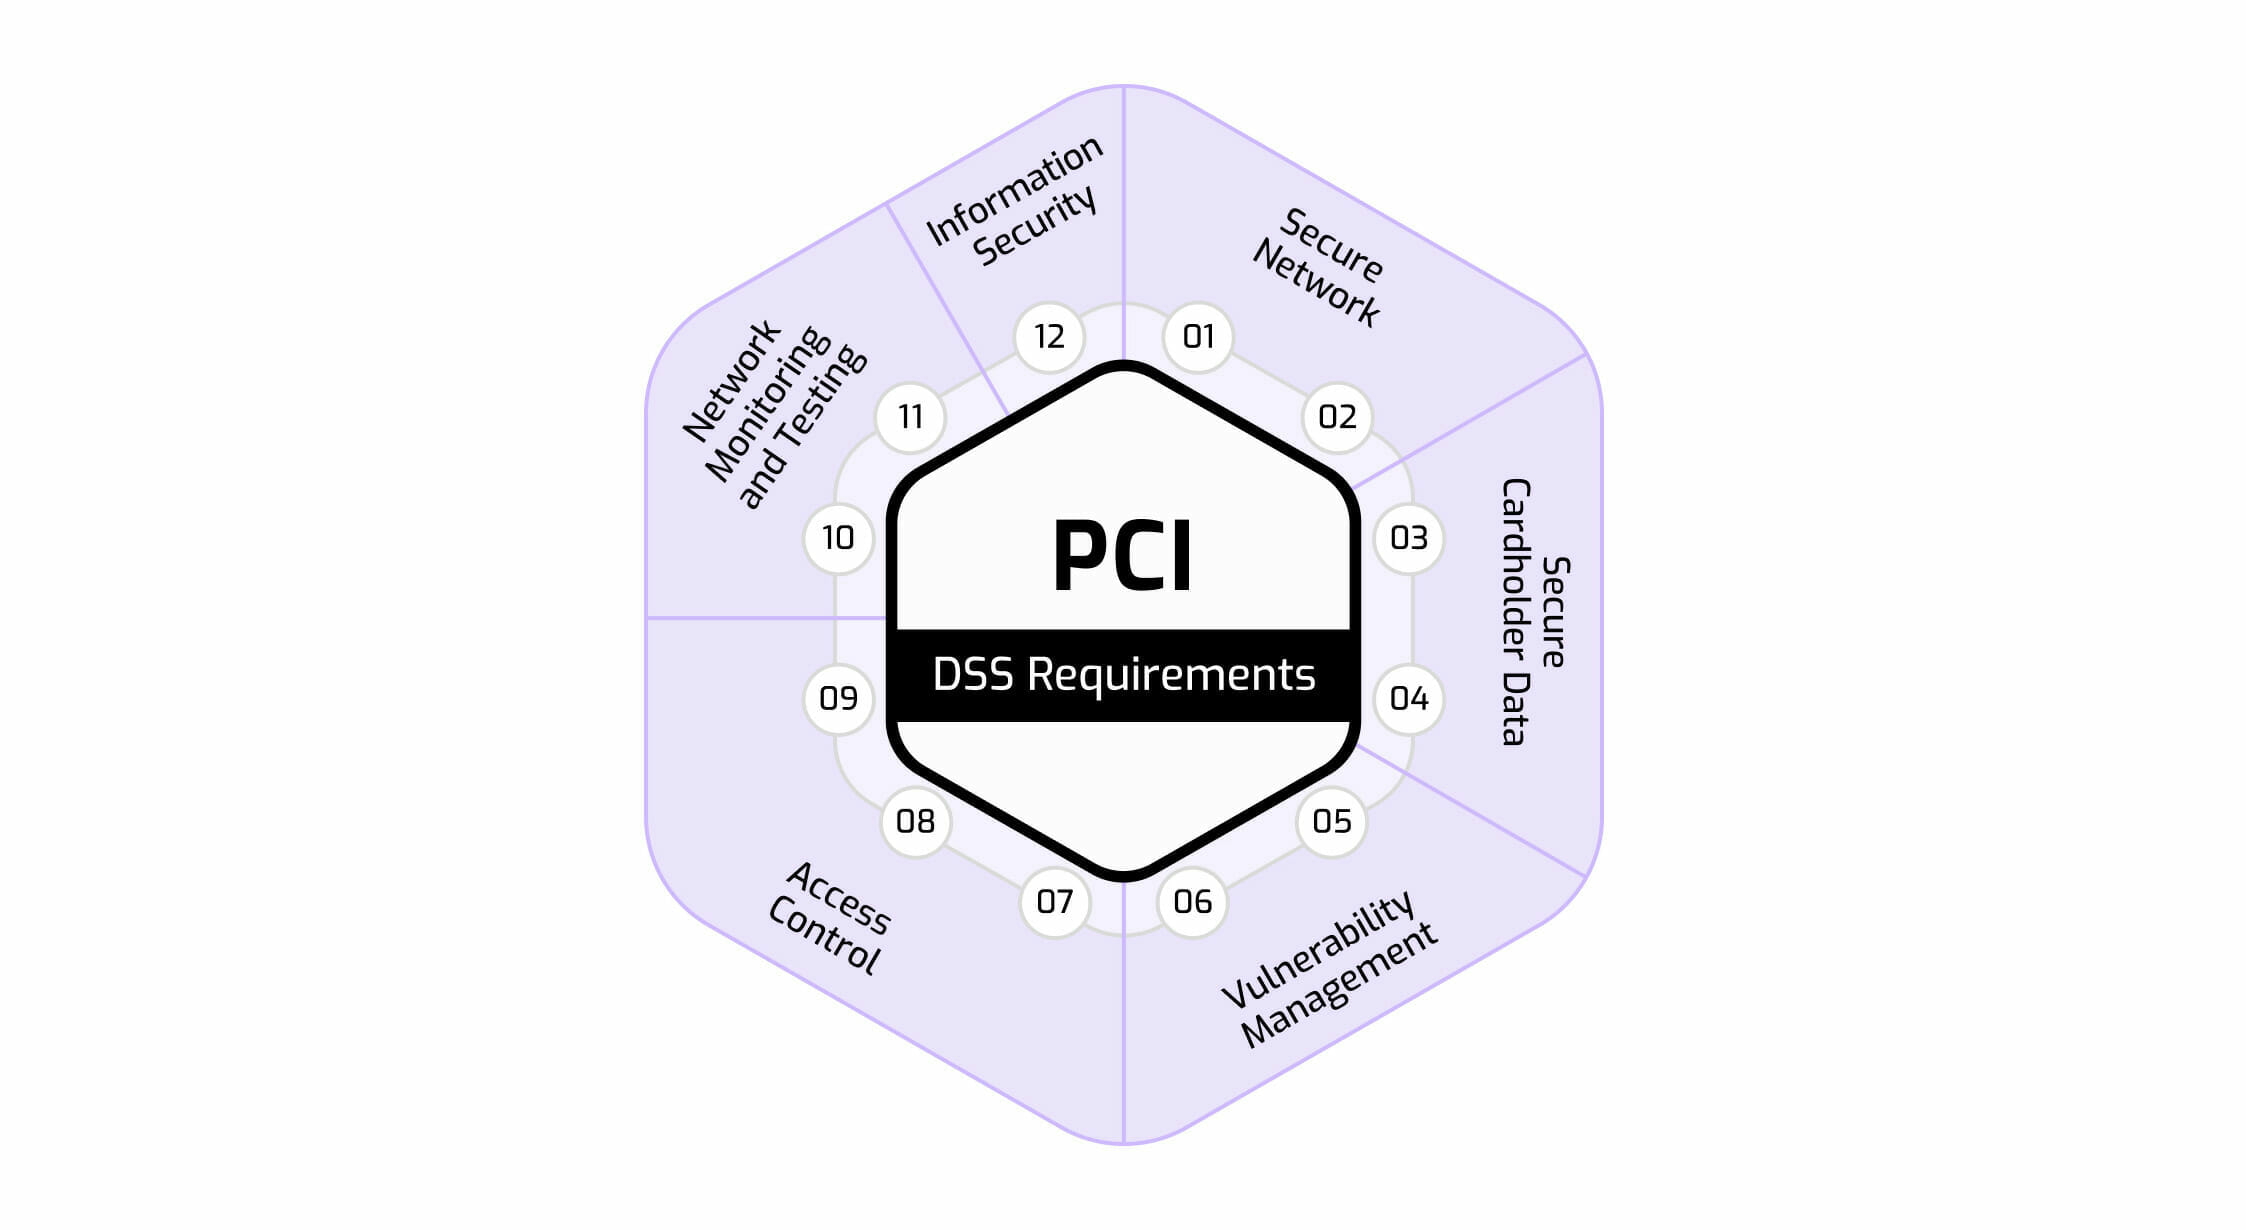
12 PCI DSS Compliance Requirements - Cycode
PCI DSS Compliance Requirements Checklist - DNSstuff

PCI Compliance Checklist: How to Achieve Compliance in 2023
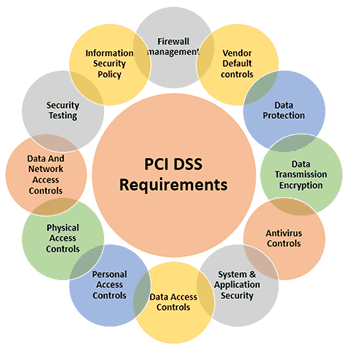
Crowdsourced Penetration Testing and PCI DSS Compliance | Cobalt

PCI DSS Requirement 5 Explained - PCI DSS GUIDE

PCI DSS Compliance: A Brief Overview

PCI Data Security Standard 3.0, Fully Explained
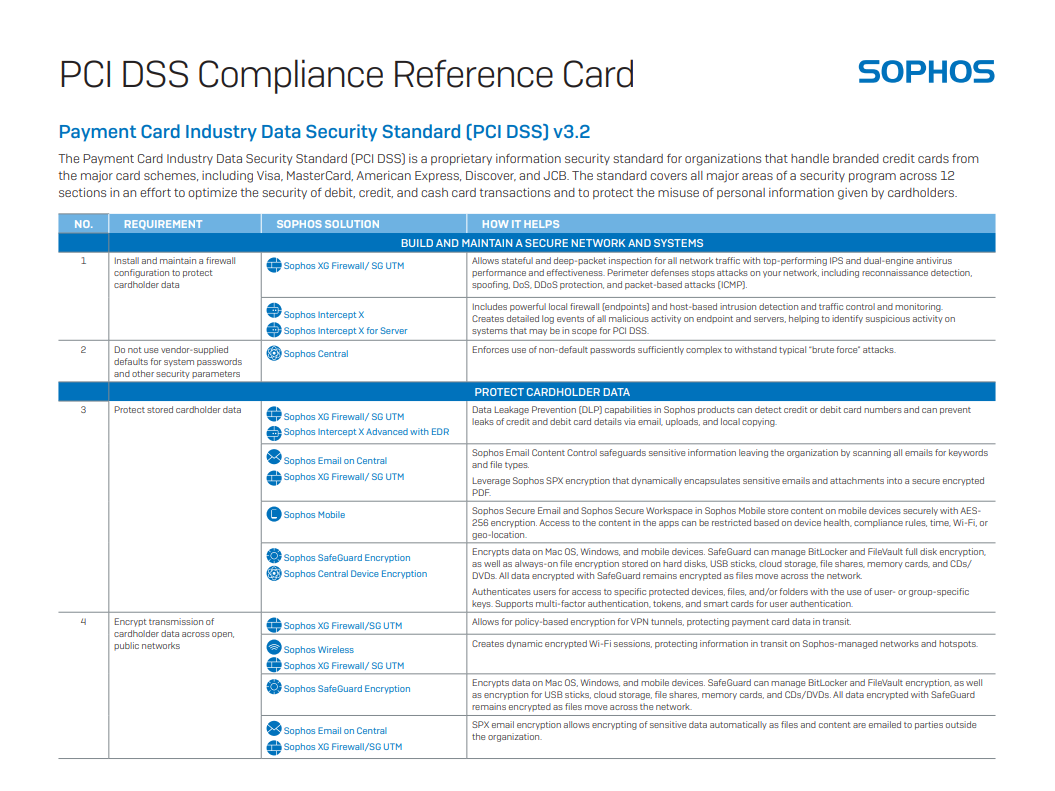
Get Your Hands on the Freshly Updated PCI DSS Compliance Card ...
What Are PCI DSS Standards? — RiskOptics
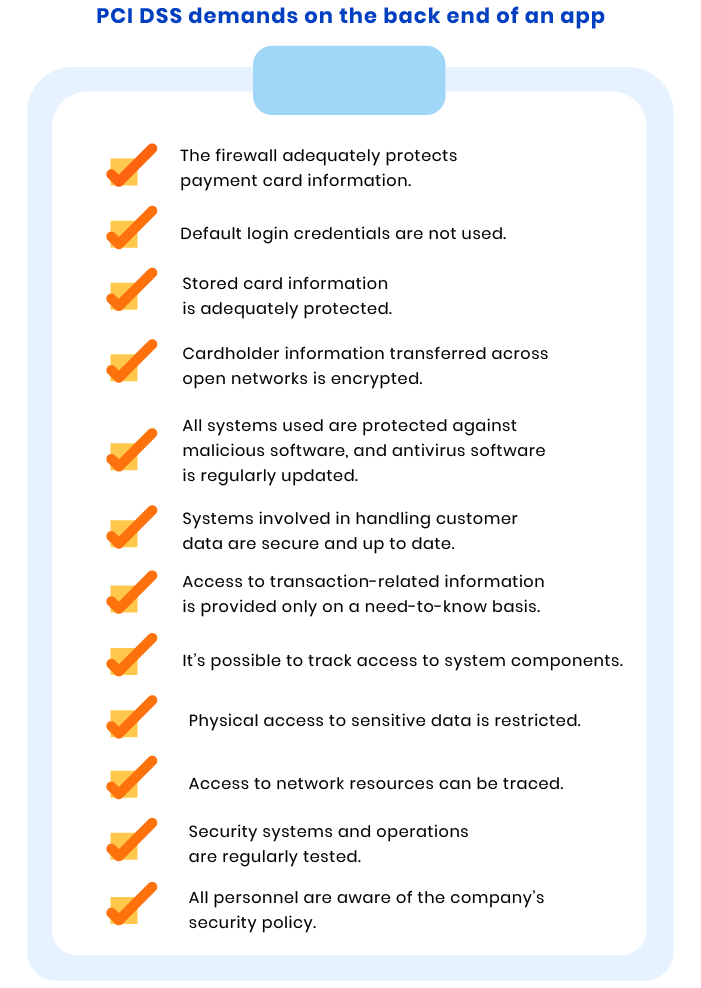
A Full PCI DSS Requirements Checklist for Your Application's ...

PCI Requirement 5: Protecting Your System with Anti-Virus

PCI Compliance Levels: A Complete Guide | Softjourn, Inc ...

5 Key Requirements for PCI DSS 4.0 Compliance

5 Tips for a Successful PCI DSS Compliance Strategy ...
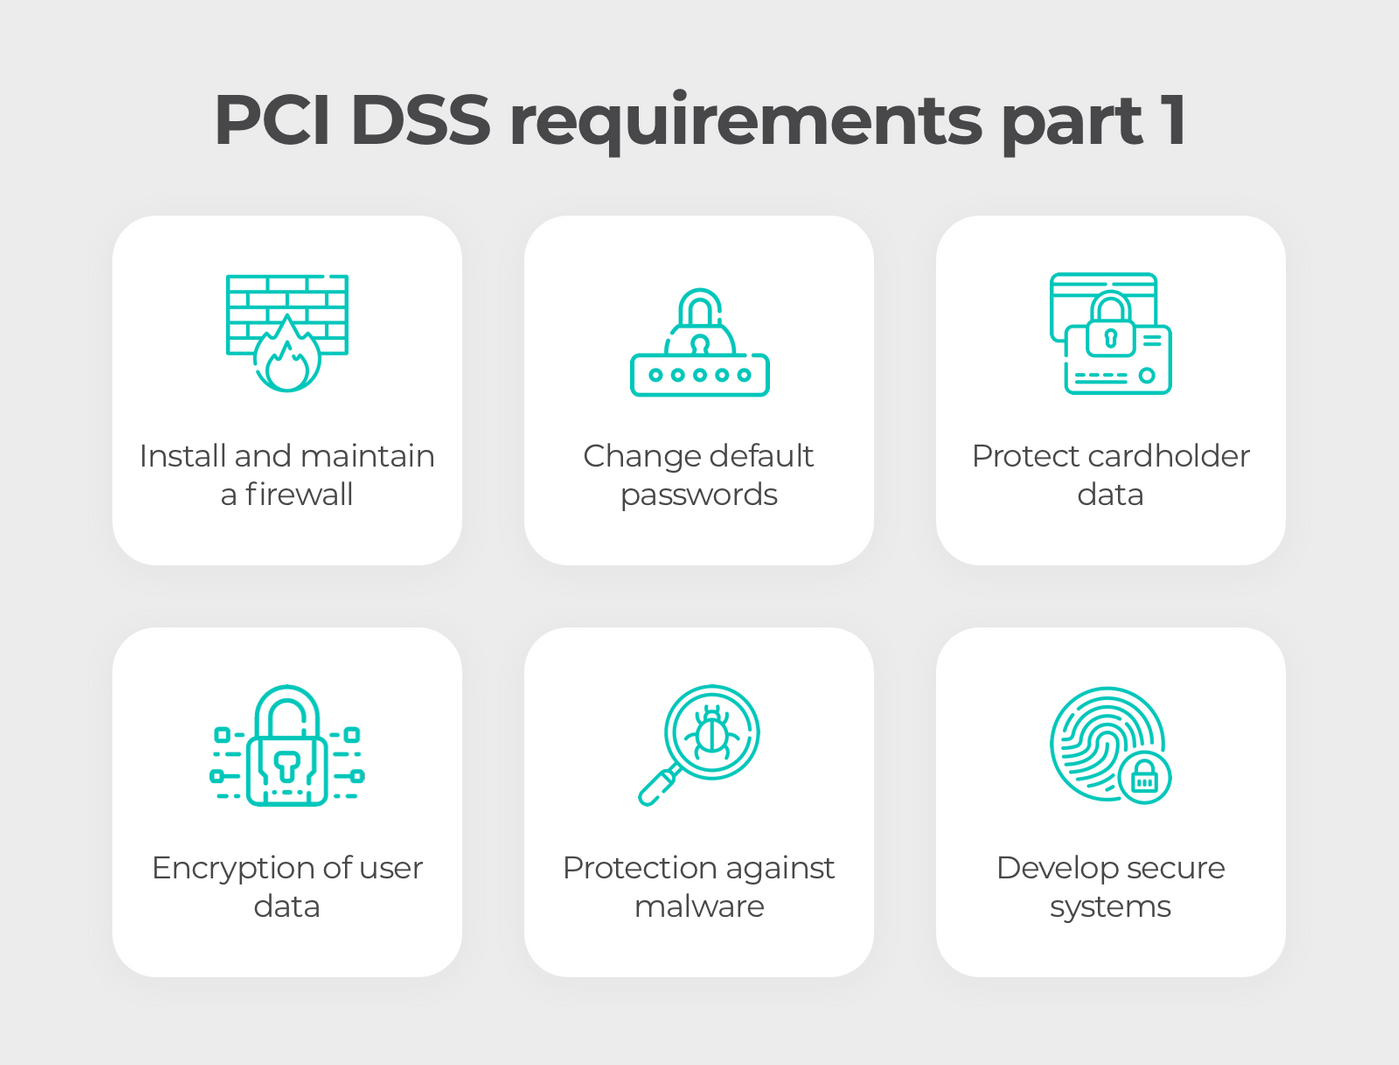
PCI DSS Compliance Requirements: All Regulations Explained

How To Make PCI-DSS Compliant App And Ensure Online Payments ...
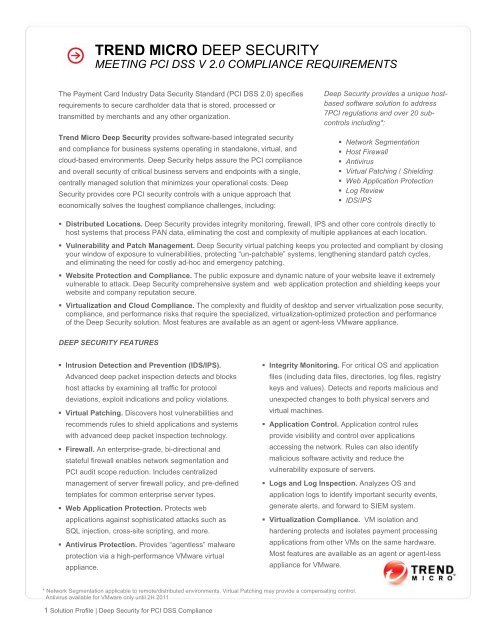
Payment Card Industry (PCI) Data Security Standard - Trend Micro

Key PCI DSS 4.0 Requirement Updates

Do you comply with PCI? — 5c Services
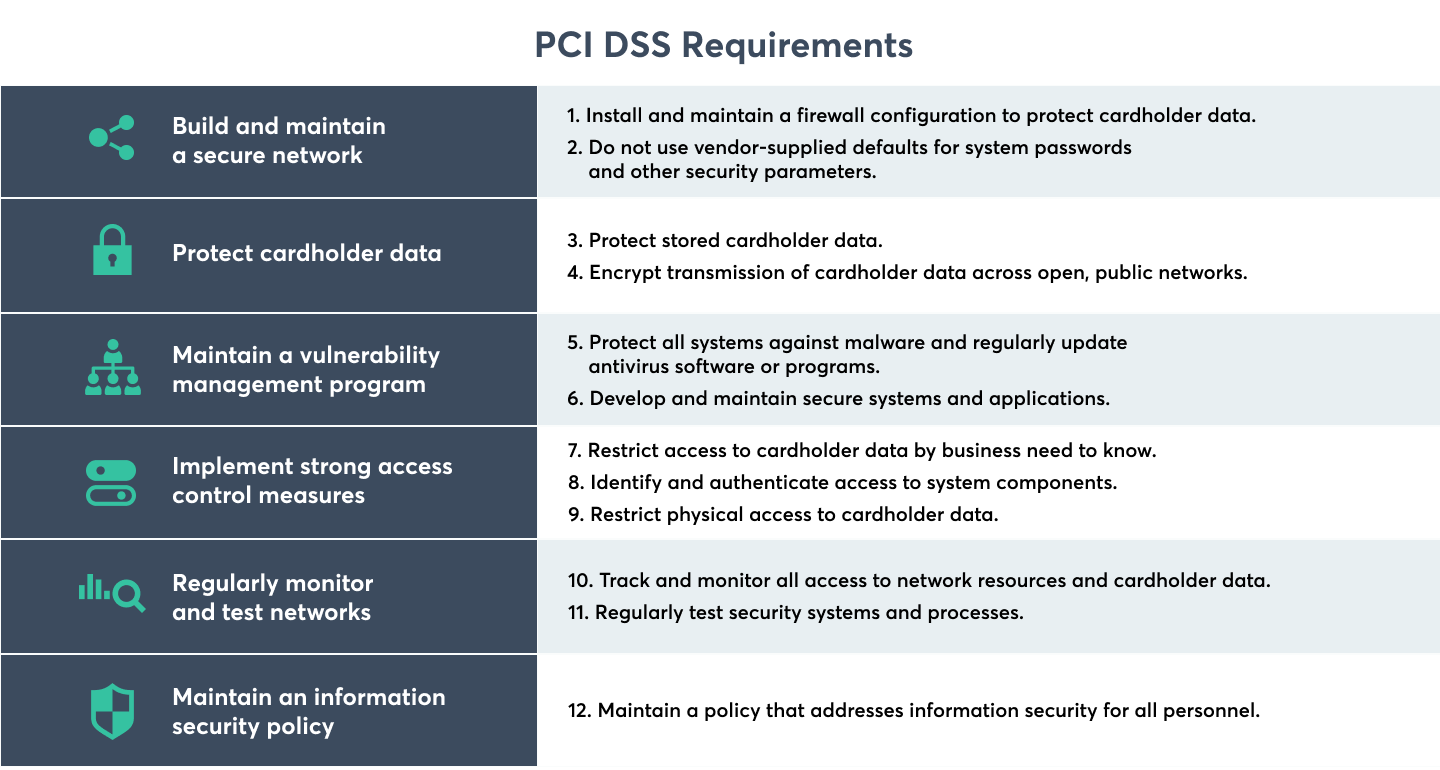
PCI DSS Compliance: A Guide for E-Commerce Businesses | Very ...
PCI DSS Compliance Requirements Guide & Checklist | Sucuri
Hillstone Security Solutions – PCI DSS 3.2.1 Compliance 1 ...

PCI DSS Penetration Testing | Compliance Test Services

What are the 12 requirements of PCI DSS Compliance?
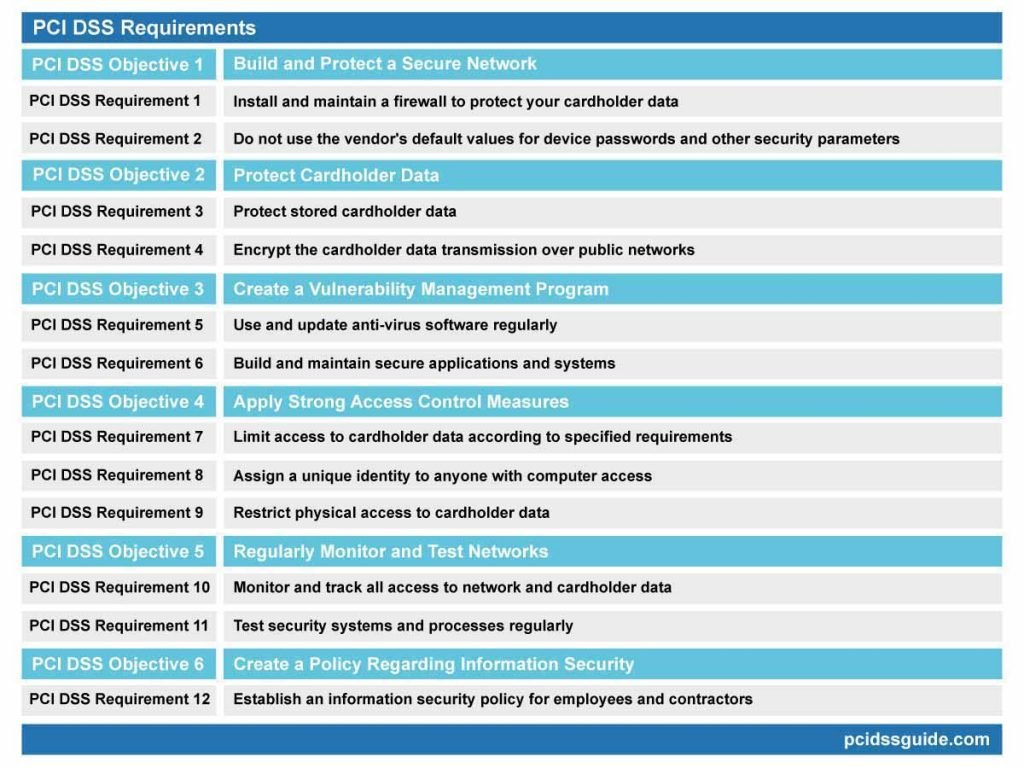
PCI DSS Requirements - PCI DSS GUIDE

PCI compliance — its standards and best practices

All you Need to Know About PCI Compliance
PCI SSC Bulletin on Malware Related to Recent Breach ...
PCI Compliance | ManageEngine Endpoint Central

Ditch Typical Anti Virus for True PCI Requirement 5 Compliance

A Complete PCI DSS Compliance Guide for midsized Businesses ...

Solutions for PCI DSS Compliance
0 Response to "44 pci dss antivirus requirements"
Post a Comment